
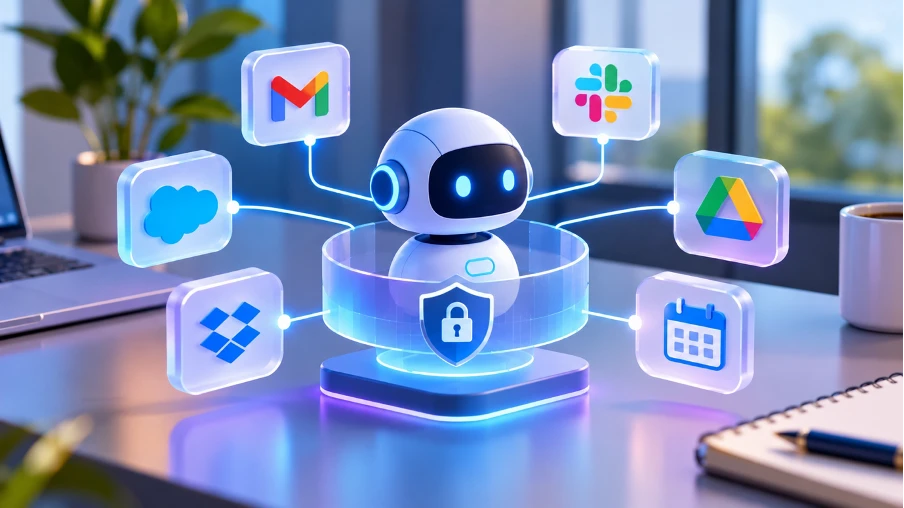
You ask an AI agent to prepare a client update. It checks your inbox, looks through the CRM, pulls figures from a spreadsheet and creates a draft in Google Docs. Five minutes later, the report is ready.
Convenient? Absolutely. But consider what happened during those five minutes.
The agent accessed customer information, read private emails, retrieved financial figures and passed information between applications. You approved the task, but did you know exactly which records it would open or where the information would go?
That question deserves attention as businesses give AI agents access to more of their daily work.
One Task Can Involve Several Data Transfers
A traditional chatbot usually works with information supplied directly by the user. An AI agent connected to workplace applications can retrieve additional material, follow instructions and carry out actions through those services.
Take a sales agent preparing a weekly report. It might read customer conversations, examine deal values, retrieve meeting notes and send the finished document to a manager.
Each application has its own permissions, data handling policies and security settings. Connecting them creates opportunities for information to move between systems that were previously managed separately.
The network connection matters as well. An employee running agents from home or while travelling may rely on networks outside the company’s control. A vpn for business can help protect traffic between the employee’s device and the VPN server.
However, an encrypted connection doesn’t stop an agent from sending information to an application it shouldn’t be using. Companies still need to control which services the agent can contact and what it is authorised to share.
Permissions Can Become Difficult to Track
When connecting an AI agent to an application, users are often asked to approve several permissions at once.
Some integrations only need to read information. Others request permission to create, modify or delete records.
Imagine giving a scheduling agent access to your calendar. Reading availability makes sense. But should it also be able to delete meetings or send invitations to external contacts without asking?
The same problem appears with cloud storage, email and CRM platforms.
Before approving an integration, examine the requested permissions. Use read-only access where possible, restrict the folders or records available to the agent and avoid connecting administrator accounts unnecessarily.
Data Without Context Can Lead to Bad Decisions
There’s another problem that has little to do with hackers.
Two AI agents can access the same information and reach different conclusions because they don’t understand the business rules behind it.
A recent VentureBeat article on business context examines how agents working across enterprise systems can make conflicting decisions even when their underlying data is accurate.
Consider a customer whose account shows an overdue payment. A sales agent might recommend contacting them about a new offer. A finance agent may flag the account for collection. Neither necessarily knows that the customer has already agreed to a revised payment schedule.
Connecting more databases won’t automatically resolve that misunderstanding.
Agents need access to relevant policies and enough context to interpret information correctly. They also need boundaries around decisions that require human approval.
Find Out What Gets Stored Along the Way
Completing a task doesn’t necessarily mean the information disappears.
An agent may generate logs, maintain conversation history or pass information through external services. Developers and business users should review these records and understand how long they are retained.
AutoGPT has previously examined this issue in its article on tracing agent data, including the importance of examining what an agent actually does during a task rather than relying entirely on its stated permissions.
For businesses handling customer records, contracts or confidential documents, this visibility becomes particularly important.
Start With Smaller, Controlled Workflows
Giving an agent access to every workplace application might seem efficient, but it makes mistakes harder to investigate.
Start with a limited task. Connect only the necessary applications, use test data where practical and inspect the results before expanding access.
Keep records of integrations and remove permissions when they are no longer needed. For actions involving payments, customer information or important business records, retain human approval.
AI agents become more useful when they can work across applications. That usefulness also makes their access worth examining carefully.
Before connecting another tool, ask a simple question: does the agent really need to see everything that application contains?
